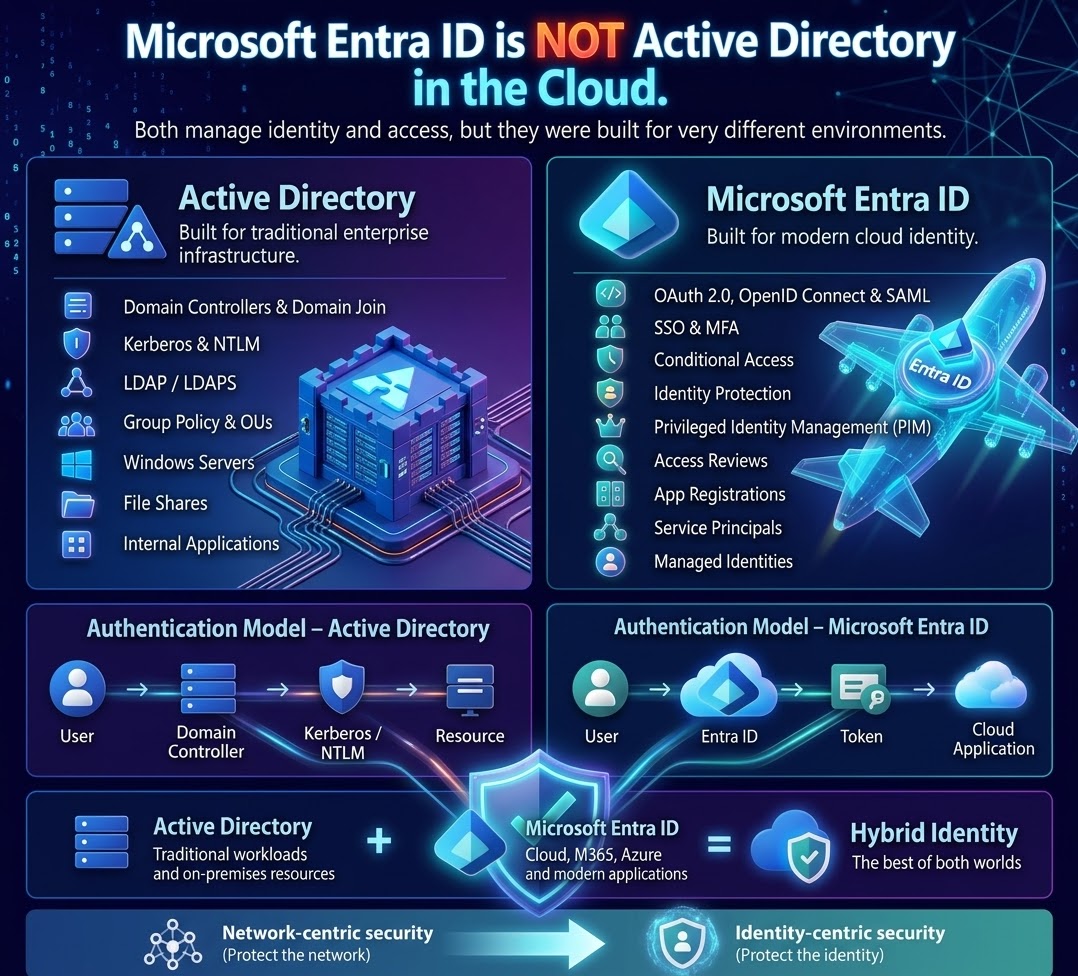
Microsoft Entra ID is NOT just Active Directory in the Cloud
Microsoft Entra ID is NOT just "Active Directory in the Cloud.
One of the most persistent misconceptions in identity and security architecture is assuming Entra ID is simply a lift-and-shift version of traditional AD.
They were architected for fundamentally different paradigms:
🔹 Active Directory (On-Premises):
- The Foundation: Built for the traditional enterprise perimeter and network boundary.
- Protocols & Control: Relies on Domain Controllers, Kerberos, NTLM, and Group Policies (GPOs).
- Security Model: Network-centric — if you breached the network, you owned the domain.
🔹 Microsoft Entra ID (Modern Cloud Identity):
- The Foundation: Engineered natively for cloud, SaaS, and borderless enterprise workloads.
- Protocols & Control: Speaks modern web standards (OAuth 2.0, OpenID Connect, SAML) with cloud-native primitives like Service Principals and Managed Identities.
- Security Model: Identity-centric — identity is the new firewall, enforced dynamically through Conditional Access, Risk-Based Identity Protection, and PIM.
The enterprise reality is rarely all-or-nothing. Hybrid Identity bridges both worlds, ensuring on-premises legacy systems remain resilient while modern cloud workloads scale securely under a unified Zero Trust strategy.
Are you still treating your cloud identity architecture like an on-prem domain?
#MoamenHany #MVP #MVPBuzz #MicrosoftMVP #Azure #CloudSecurity #MicrosoftEntra #EnterpriseArchitecture #Identity #ZeroTrust #TechLeadership #AlnafithaIT